
Activate Identity Operations
Automate the operational work across your existing identity ecosystem.
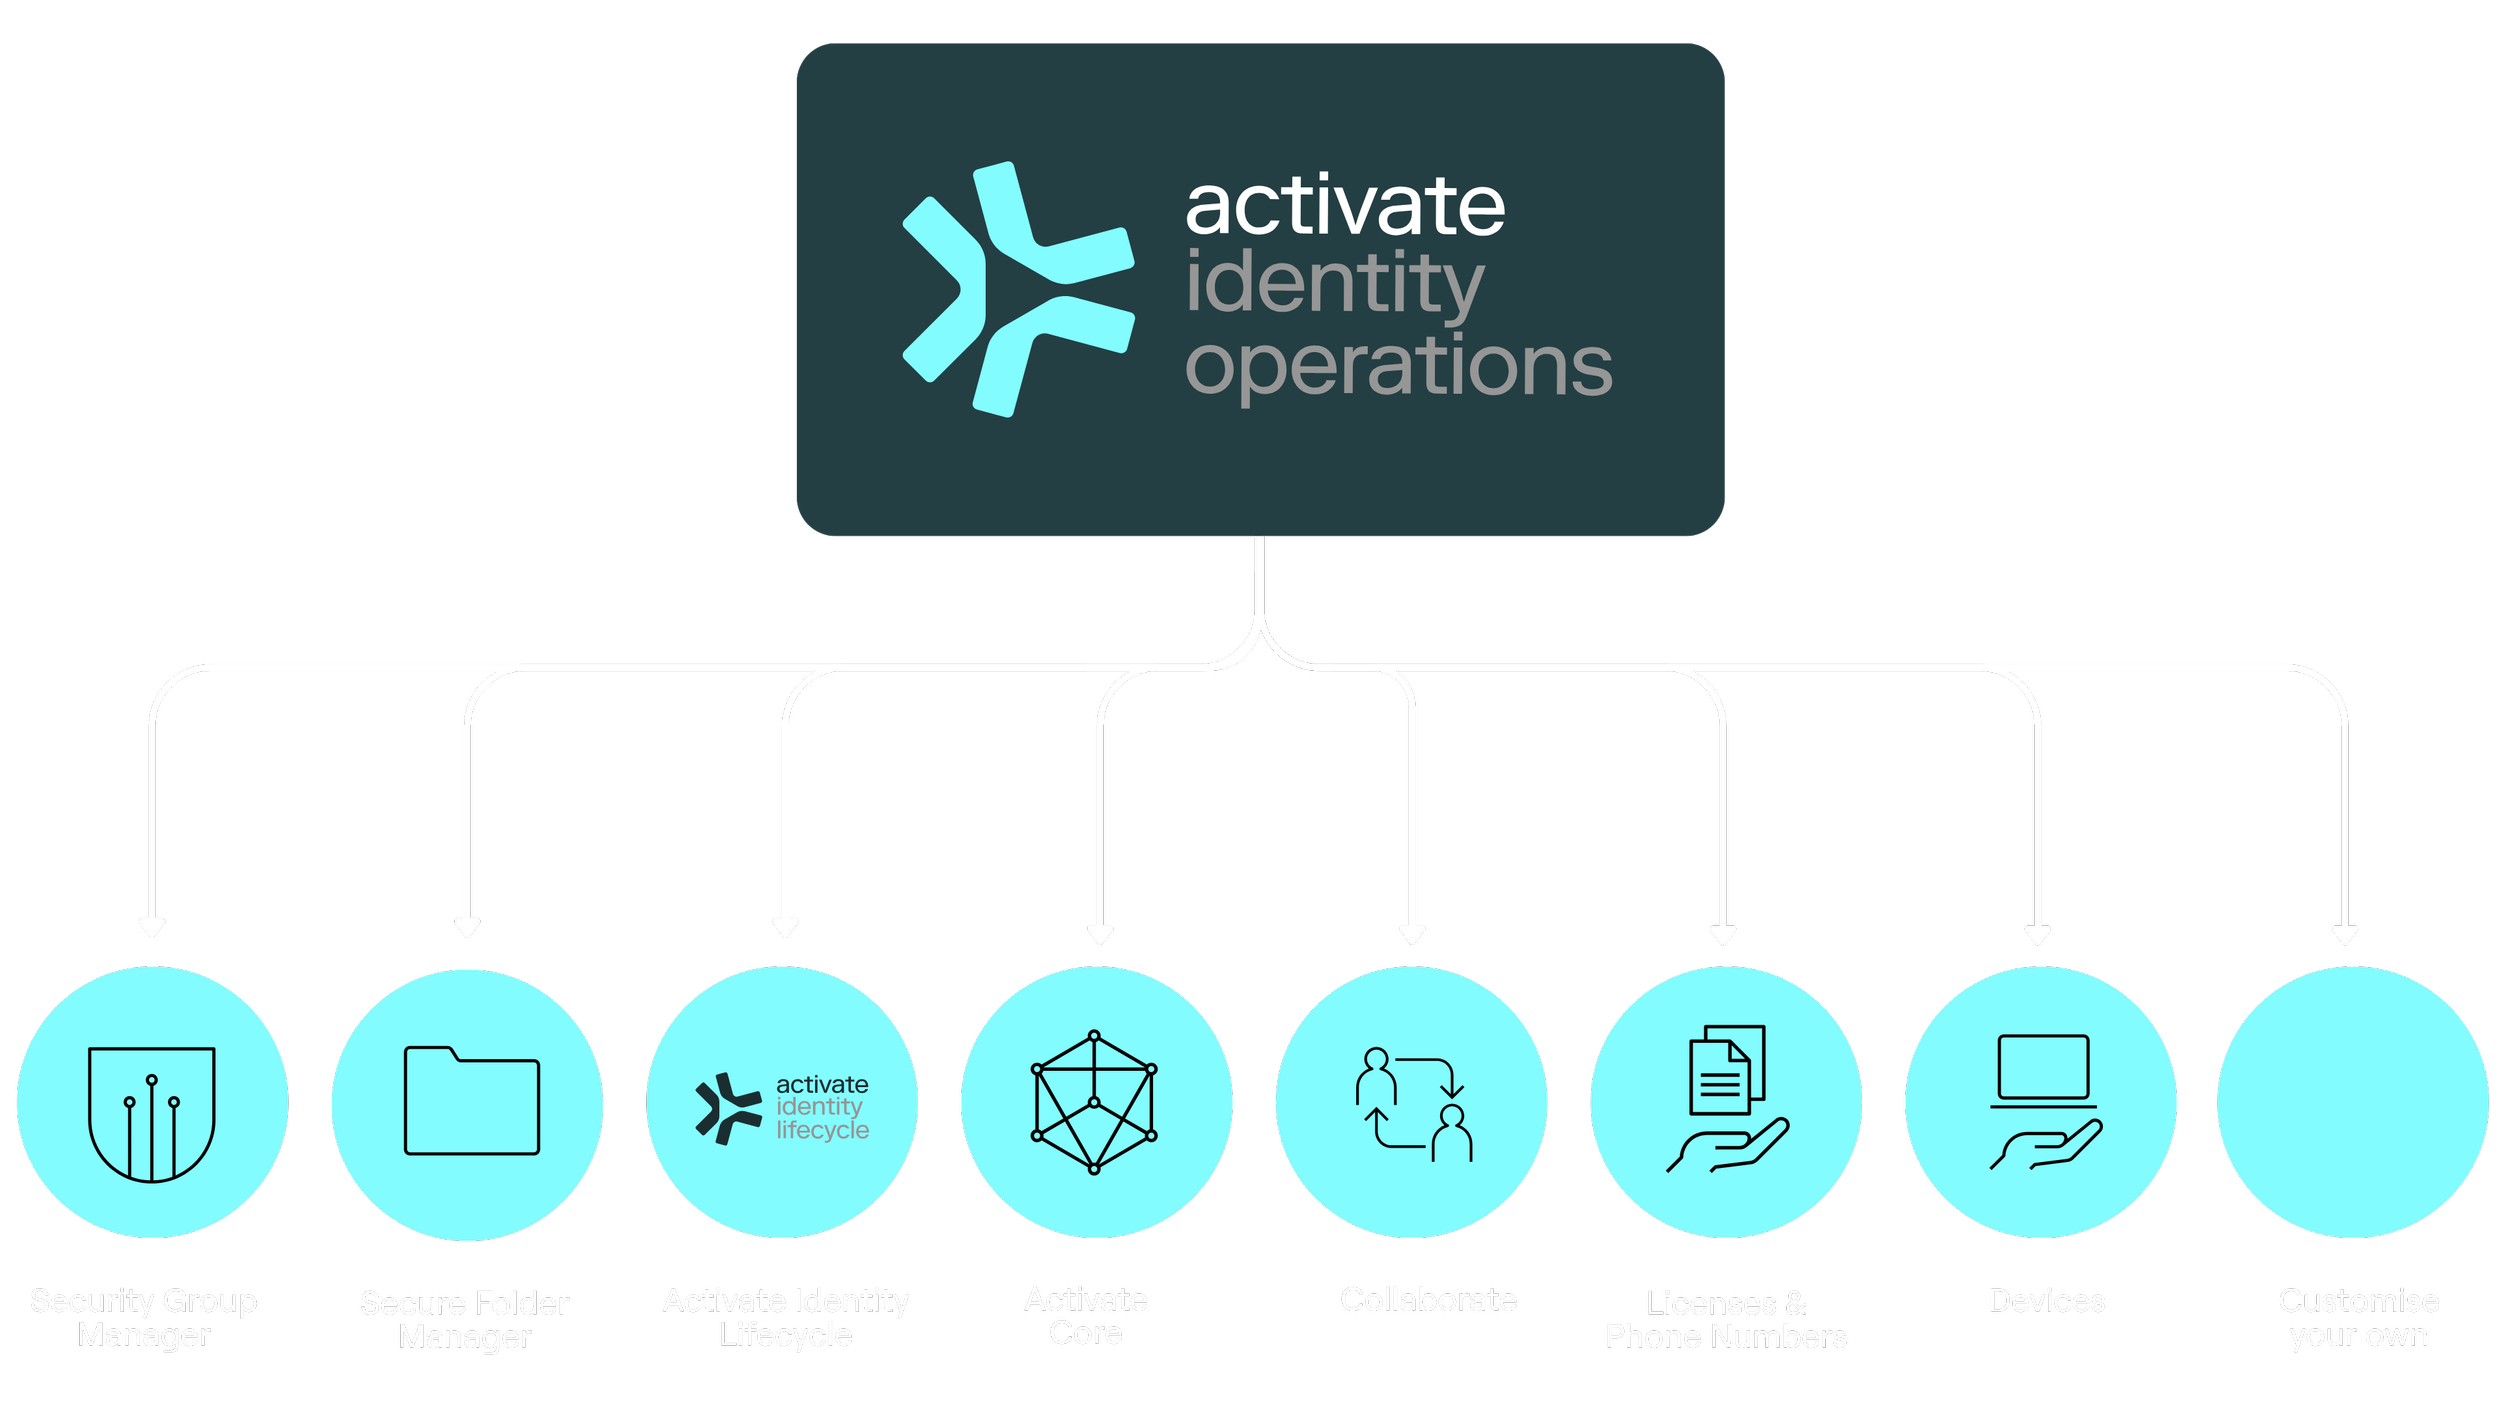
The complete solution for Enterprise Identity Operations. Activate automates approvals, provisioning, fulfilment and identity lifecycle execution across complex enterprise environments.
Identity governance platforms determine who should have access. Activate ensures those decisions are executed consistently across your workforce, systems, applications and digital assets.
Activate is built for organisations where identity is operationally complex.
Enterprise teams managing complex identity lifecycle processes, preparing for AI adoption, and non-human identities.
Teams extending Microsoft Entra, Active Directory or ServiceNow with enterprise identity automation.
IAM and GRC teams supporting audit, compliance and governance.
Security teams reducing identity risk and improving operational control.
How Activate Identity Operations works.
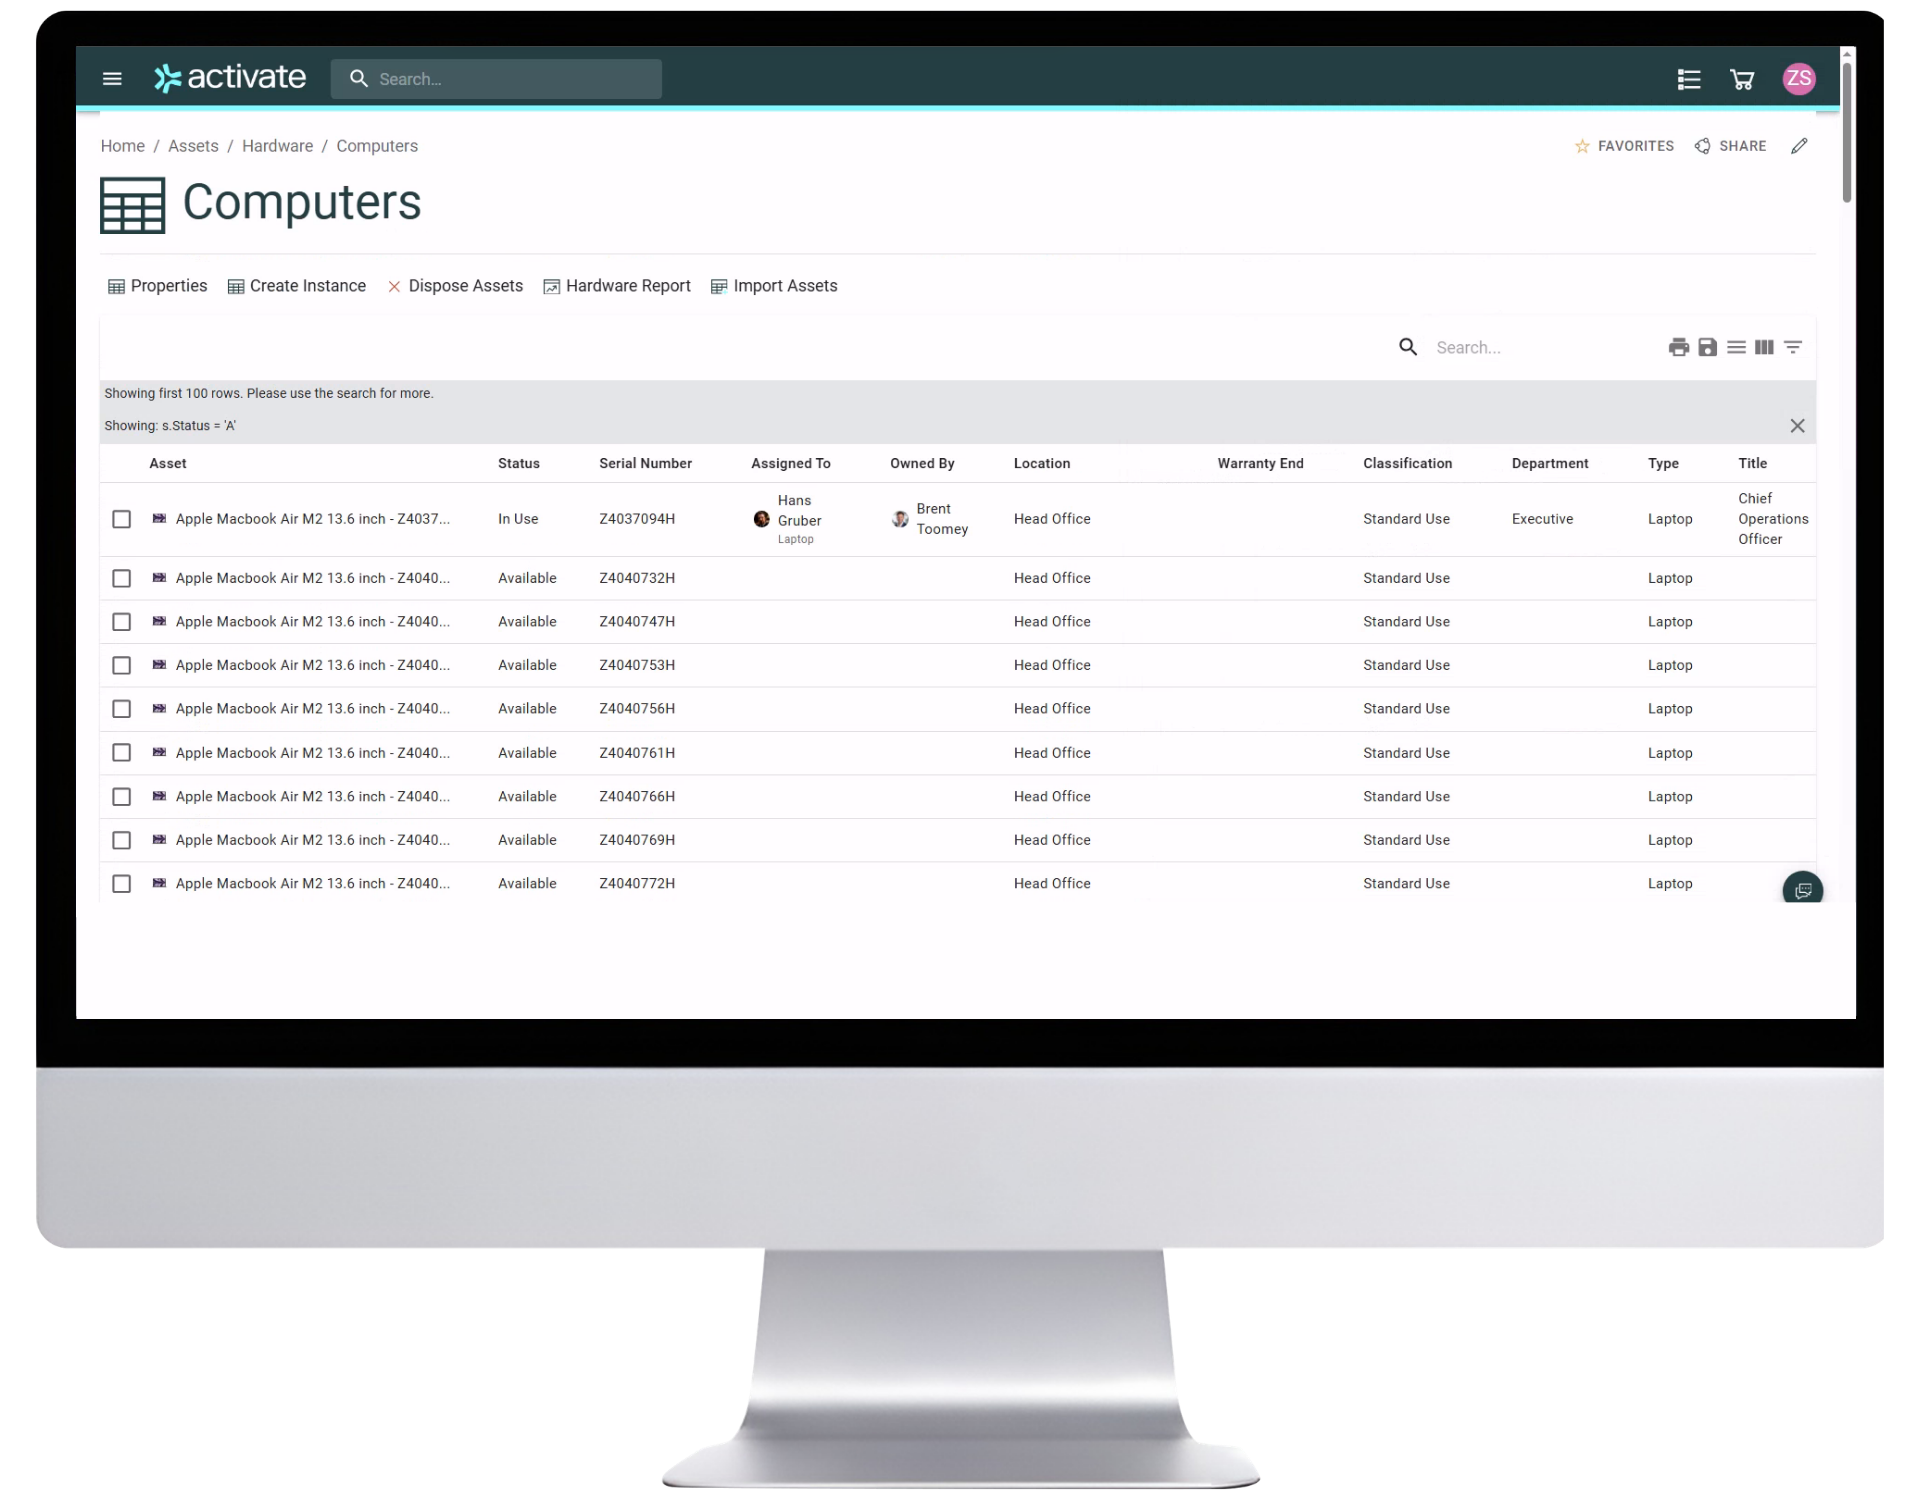
Enterprise identity work is rarely contained within one system. Approvals, provisioning, fulfilment and downstream tasks often span multiple teams and technologies.
Activate provides an operational layer across that environment, coordinating identity changes from request and approval through to execution and audit.
From a single platform, you can automate activity across users, applications, devices, digital assets and business workflows while maintaining consistency and visibility.
Reduce manual identity work while strengthening operational control.
Automate recurring identity work while improving consistency, security and auditability. With Activate you can:
Automate approvals across business and IT teams
Coordinate provisioning and fulfilment across multiple systems
Reduce manual requests and service desk effort
Apply consistent processes across hybrid environments
Produce continuous audit evidence and operational traceability
Reduce over-privileged access through controlled lifecycle processes
Support ISO 27001 and other governance frameworks through consistent execution
Activate Identity Operations is the complete solution for Enterprise Identity Operations.

Identity changes rarely affect only one system. Activate coordinates operational work across:
Users
Service accounts & non-human identities
Applications
Devices
Security groups
Shared mailboxes
Distribution lists
Licences
Digital assets
Business workflows
Custom enterprise processes
Connect HR, Microsoft Entra, Active Directory, ITSM and business applications into coordinated workflows without replacing the platforms you already use.
Built for hybrid and cloud environments, Activate extends automation across the systems you already run, without replacing existing identity investments or taking on a large transformation programme.
Built to complement your existing identity platform
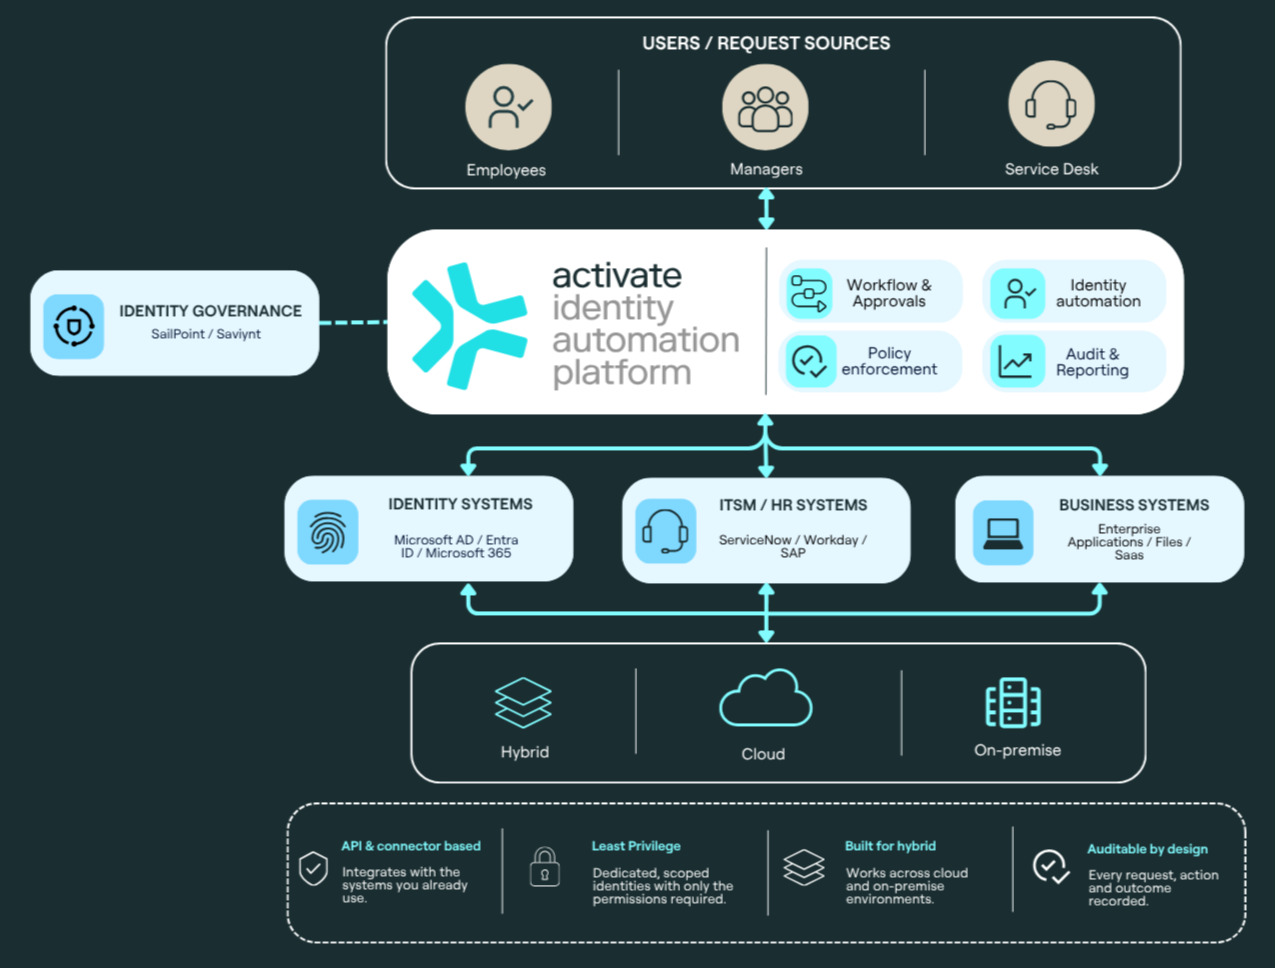
Activate works alongside the technologies you already use, including
Microsoft Entra ID
Active Directory
Non-human identity platforms
ServiceNow
HR systems
Identity Governance platforms
Business applications
Cloud and on-premises environments
Activate fills the operational gap between identity decisions and their execution across these systems.
“The solution has significantly improved our ability to manage identity lifecycle processes in a consistent and controlled way.”
- Government Identity & Access Manager
Why do identity operations matter?

Creating an account is only one step in the identity lifecycle. Real enterprise identity involves:
Business approvals
Provisioning
Fulfilment
Notifications
Security groups
Shared resources
Device allocation
Downstream application updates
Audit evidence
Exception handling
Activate orchestrates these activities into one coordinated identity process, helping organisations reduce manual effort while improving operational visibility.
Trusted identity operations across your enterprise.
Reduce enterprise identity risk through governance across identities, systems and assets.
REDUCE GOVERNANCE GAPS, STRENGTHEN SECURITY CONTROL ACROSS COMPLEX ENVIRONMENTS.
Controls are explicit, approvals are consistent, and evidence is always available. Reduce over-privileged access and identity-related operational risks.
Prevent inconsistent approvals, and produce defensible, continuous audit evidence.
Improve compliance with regulatory and security requirements lincluding ISO 270001. Learn more here
Preparing your organisation for operational AI?
ACTIVATE PROVIDES A UNIFIED OPERATIONAL LAYER ACROSS YOUR DIGITAL ENVIRONMENT.
Gain visibility across identities, systems, applications, devices and assets while automating the work that happens after identity decisions have been made.
The result is less manual work, faster identity lifecycle execution, better operational consistency, improved audit readiness, and greater value from existing identity investments.
Learn more about enterprise identity operations.
Unified identity operations across access, lifecycle, and digital workspace.
AI ASSISTANTS AND AI AGENTS ARE NON-HUMAN IDENTITIES THAT RELY ON THE IDENTITIES, PERMISSIONS AND LIFECYCLE PROCESSES ALREADY OPERATING WITHIN YOUR ORGANISATION.
As AI adoption grows, trusted identity operations become increasingly important.
Activate helps organisations automate the operational foundations that support secure, well-governed AI adoption.
Explore features
-
Automates the creation, maintenance, and governance of security group memberships by aligning access with organisational roles, attributes, and policies.
Enforces least-privilege access across systems by dynamically updating memberships, while removing manual administration and reducing privilege sprawl.
Delivers full auditability, scalability, and clear visibility into who has access and why, strengthens compliance and gives IT teams confidence in their access governance.
-
Automate access & governance across file shares and cloud storage. Permissions stay aligned to business structure, helping prevent over exposure of sensitive data.
-
Core engine of the base platform. Includes orchestration engine, approval engine, analytics, auditing, Microsoft integration, connectors, and security boundary.
-
Activate Access Automation replaces manual requests and provisioning with governed workflows that connect directly to your systems.
Users request access through a self-service portal or existing ITSM tool. Activate evaluates each request based on role and context, then approves automatically or routes for approval. Once approved, access is provisioned across AD, Entra ID, and business applications.
Access can be time-bound and removed automatically.
It works alongside Activate Identity Lifecycle by handling on-demand access requests, while lifecycle automation manages joiner, mover and leaver events, together delivering consistent, end-to-end identity control.
-
Activate Identity Lifecycle builds on Access Automation by extending control from individual requests to the full workforce lifecycle.
When users join, move, or leave, Activate automatically provisions, updates, or removes access across business systems based on role and organisational data.
As roles change, outdated access is removed and new access applied automatically. Leaver events trigger immediate de-provisioning.
Together with Access Automation, it ensures both requested and lifecycle-driven access are handled consistently, reducing manual effort and maintaining continuous control.
-
Governs and automates Microsoft Teams at scale by enforcing policies for team creation, naming, membership and lifecycle, reducing unmanaged growth and administrative overhead.
Enables automated provisioning from templates or triggers, synchronises memberships from authoritative sources, applies governance rules including approvals, naming conventions and expiry.
Provides auditing and self-service capabilities to keep Teams secure, compliant and aligned with business requirements.
Teams environments stay structured, with appropriate access and lifecycle management across the organisation.
-
Automate the assignment and management of software licenses, subscriptions and phone numbers.
Ensure users receive the right tools based on their role, while unused licenses are automatically reclaimed or cancelled when access changes.
Reduces waste, controls costs, and maintains clear visibility over software usage and entitlements.
-
Automate device assignment and lifecycle management as part of your identity processes.
Activate Devices ensures users receive the right hardware based on their role, while devices are reassigned or decommissioned as roles change.
This improves visibility, reduces manual effort, and keeps your digital workspace aligned with workforce changes.
-
Purchase as part of Activate Security Extension. Activate Privileged Account Management (PAM) delivers secure, policy-driven control of high-privilege accounts through self-service workflows that operate natively within the Activate platform. It automates the lifecycle management, approval, and review of privileged accounts, enforcing just-in-time access, and full auditability across on-premises and cloud environments. By unifying governance, automation, and compliance, Activate Privileged Account reduces standing privileges, improves security posture, and enables business owners to manage privileged accounts efficiently without ongoing IT involvement.
-
Customers can apply Activate’s identity management automation to almost any assigned asset; security cards, meeting rooms, vehicles or any specialist equipment. If an item needs an owner, approval, lifecycle and audit trail, Activate can automate how it is assigned, changed, reclaimed and governed.
Want to go deeper?
Still have questions? Explore architecture, deployment models, configuration, automation and operational guidance at the Activate Knowledge Centre, or speak to one of our team.
Frequently asked questions
-
Enterprise identity changes rarely happen in one system. Approvals, provisioning, fulfilment, lifecycle changes and downstream tasks can span HR, Microsoft Entra, Active Directory, ITSM tools and business applications.
Activate automates and coordinates that operational work, reducing manual hand-offs, service tickets and inconsistent processes while improving control and auditability.
-
IGA platforms help organisations determine and govern who should have access.
Activate focuses on what happens next: executing those decisions consistently across the systems, applications and workflows involved.
It automates approvals, provisioning, fulfilment and lifecycle activity across your existing identity environment. The two can work together rather than replacing one another.
-
No. Activate is designed to work alongside the technology you already use, including Microsoft Entra ID, Active Directory, ServiceNow, HR systems, identity governance platforms and business applications.
It provides an operational automation layer across those systems, helping you get more value from existing investments without requiring a large rip-and-replace programme.
-
Organisations typically see value in weeks through improved access visibility and more efficient access reviews. Time to value depends on scope and integrations, but initial use cases are deliberately low risk.
-
Activate applies approved workflows consistently and records the approvals, actions and changes that occur as identity processes are executed.
This creates operational traceability and audit evidence while helping organisations reduce inconsistent approvals, unmanaged access changes and manual processes across their identity environment.
-
Start with a high-volume identity process that still involves manual work, tickets or multiple hand-offs.
That might be access requests, joiner-mover-leaver processes, security groups, shared resources or another repetitive identity workflow. From there, automation can be extended across more systems, identity types and operational processes.
-
Yes. Enterprise identity operations increasingly extend beyond employees and contractors to service accounts, privileged accounts and AI agents.
Activate can apply controlled workflows, ownership, approvals, lifecycle processes and auditability to these identity types, helping organisations extend existing identity controls as their environment becomes more complex.