
Activate and Datacom Work With Government Agency to Replace Fragmented Identity Processes with End-to-End Automation
Customer Snapshot
Organisation: Mid-sized government department
Industry: New Zealand public sector
Environment: A diverse workforce and multiple connected identity and business systems
Jobs to be done: Automate joiner, mover and leaver processes, reduce service desk workload and make identity changes more consistent and auditable
Delivery partner: Datacom
Solution: Activate Identity Lifecycle
The Challenge
This department manages identity and access across a large and constantly changing workforce. Every new employee, role change and departure created work across multiple systems. Much of that work was manual, fragmented and difficult to see from end to end.
New accounts and access had to be provisioned. Existing permissions needed to change when people moved roles. Access had to be removed when someone left. Each task could appear routine on its own, but together they created a growing operational burden.
Manual processes took time, relied on hand-offs and increased the chance of mistakes. Employees could wait several days for the access they needed, while delays removing access for leavers created avoidable security risk.
The service desk carried much of this workload. At the same time, our customer had limited visibility into identity changes across systems and found it difficult to apply access policies consistently at scale.
The Jobs That Needed to Get Done
Our customer needed a more reliable way to:
Set new employees up with the access they needed
Update access when people changed roles
Remove access promptly when someone left
Apply identity policies consistently consistent policies across systems
Reduce repetitive provisioning work for the service desk
Keep a clear record of identity and access changes
Support a changing workforce without adding equivalent manual effort
The goal was not simply to introduce another identity tool. It was to make the work behind each employee change happen more consistently from beginning to end.
Where the Hidden Costs Were Building
The cost of manual identity operations rarely appeared as one large line item. It accumulated across many smaller activities. Every account created by hand took time. Every role change that needed several updates created another opportunity for something to be missed. Every delayed removal left access in place for longer than necessary. Every identity-related ticket added to the service desk queue.
There were also less visible costs. Employees waited for access before they could work effectively. IT teams spent time checking and correcting changes. Security and audit teams had less visibility into who had access, what had changed and whether leaver access had been removed.
As their workforce and technology environment evolved, these small points of friction became harder to manage consistently. The organisation needed identity lifecycle processes that could scale without the manual workload scaling alongside them.
The Solution: Connect the Employee Lifecycle
The agency partnered with Activate and Datacom to implement our automated identity lifecycle management solution. Activate introduced policy-driven automation across the joiner, mover and leaver lifecycle. Instead of treating each account or access change as a separate manual task, the solution connected identity activity into a consistent end-to-end process.
New employee provisioning
Role and access changes
Employee de List and default access updates
Leaver deprovisioning
Access policy enforcement
Logging and visibility across identity changes
When someone joined, the appropriate identity and access processes could begin automatically. When an employee moved roles, access could be updated according to policy. When employment ended, access removal could happen within hours rather than remaining in a manual queue for several days.
Automation also reduced the number of identity requests requiring service desk intervention. This allowed IT teams to spend less time carrying out repetitive provisioning work and more time on the tasks that genuinely required their expertise.
How Activate and Datacom Worked Together
Datacom worked alongside Activate to deliver the solution within our customer’s existing environment.
The implementation mapped identity lifecycle processes from end to end, replacing fragmented manual activities with automated, policy-driven workflows. This gave the government agency a more consistent way to manage identity changes while improving visibility and auditability across core systems.
Rather than forcing them to replace their existing technology environment, the solution coordinated identity lifecycle work across it.
“The solution has significantly improved our ability to manage identity lifecycle processes in a consistent and controlled way.” ”
The Outcome: Less Manual Work and More Consistent Identity Operations
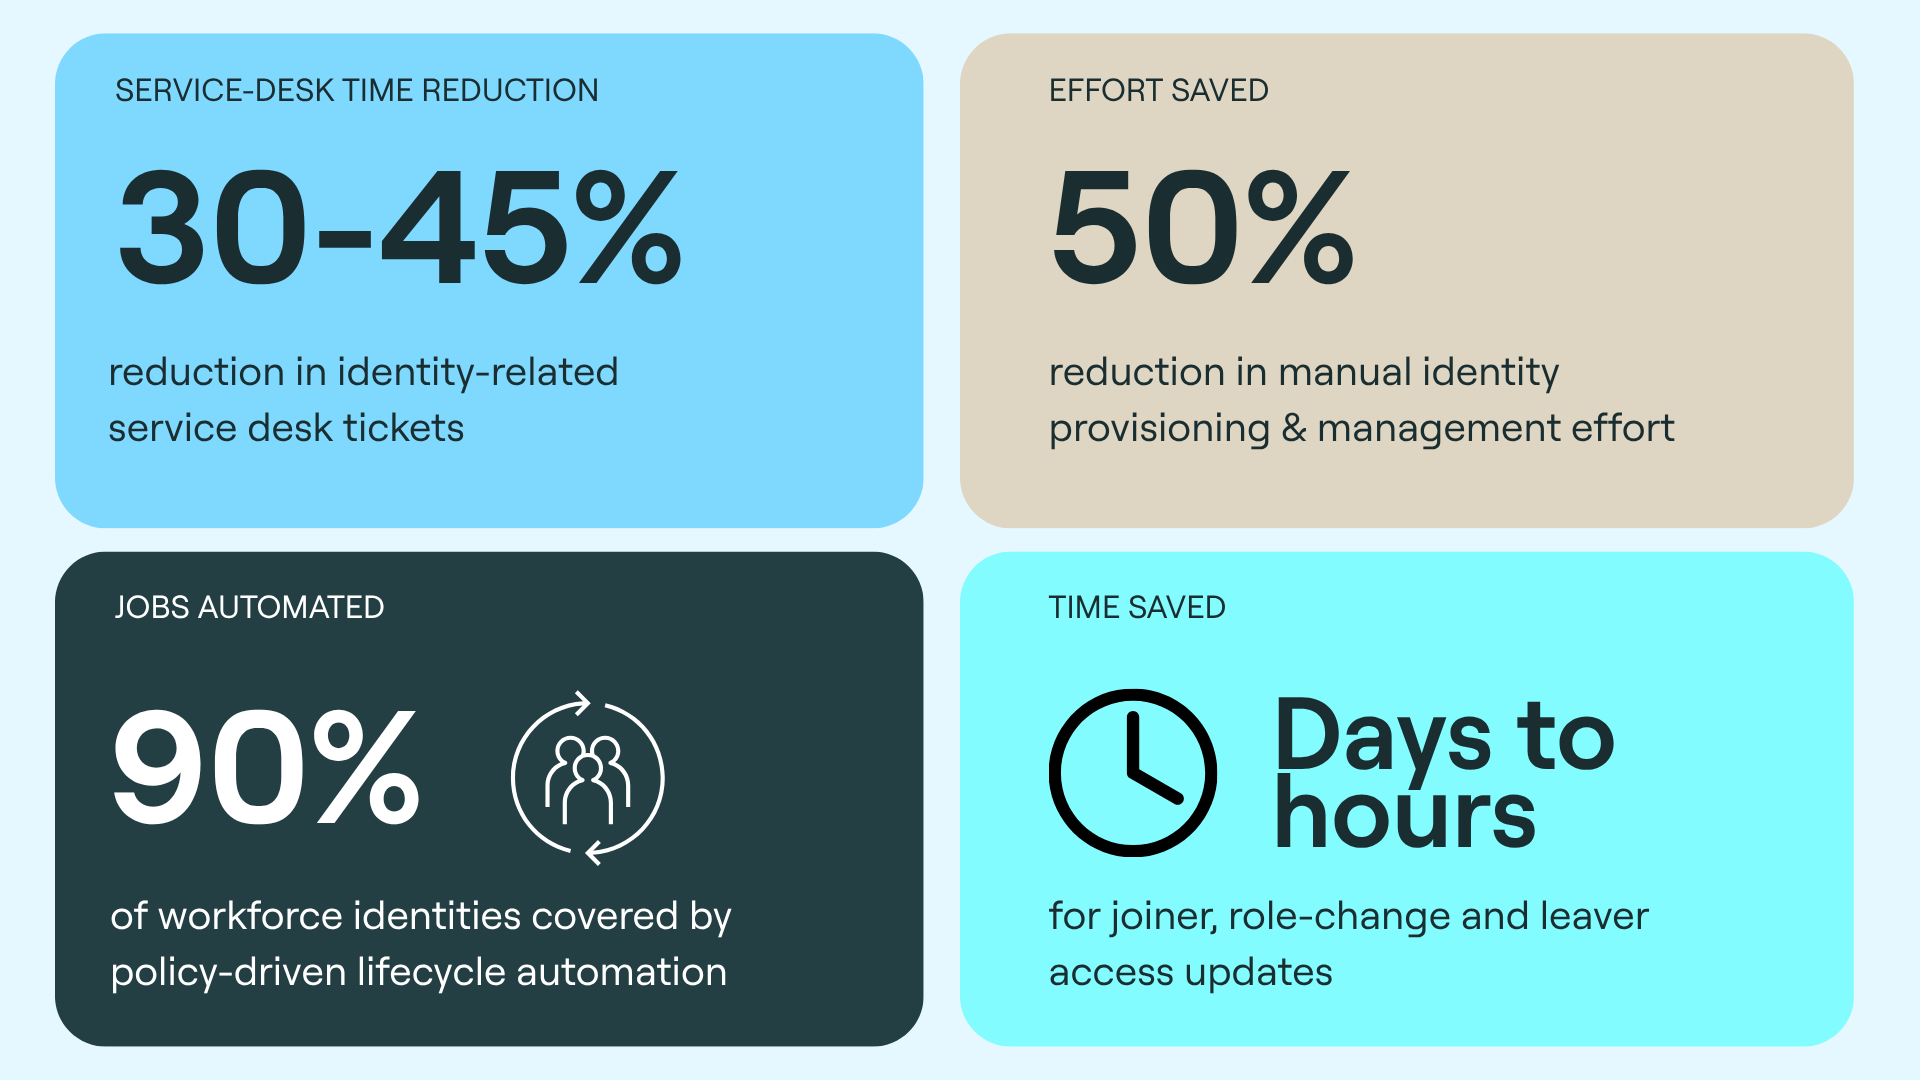
Automating the employee identity lifecycle gave the government agency a more reliable and scalable way to manage access across a changing workforce. Manual identity provisioning and management effort fell by approximately 50%. Joiner and role-change provisioning, which previously took several days, could be completed within hours.
Leaver access removal also fell from days to hours, reducing the period in which inappropriate or orphaned access could remain active. Identity-related service desk tickets dropped by between 30% and 45%. Policy-driven automation was extended to more than 90% of workforce identities, helping them apply identity processes more consistently at scale.
Key Outcomes
Manual identity provisioning and management effort reduced by approximately 50%
Joiner and role-change provisioning reduced from several days to hours
Leaver access removal reduced from days to hours
Identity-related service desk tickets reduced by 30–45%
Policy-driven lifecycle automation extended to more than 90% of workforce identities
Improved visibility and auditability of identity changesless identity changes across core systems
More consistent identity lifecycle processes
Less reliance on manual service desk fulfilment
Reduced risk from delayed or incomplete access removal
The Bottom Line
The hidden cost of identity lifecycle management was spread across hundreds of everyday tasks. A new account here. A role change there. A leaver waiting to be removed. Another service desk ticket added to the queue.
By connecting those tasks into an automated employee lifecycle, this customer reduced manual effort, shortened access delays and gave its teams better visibility into identity changes.
The result was not simply faster provisioning. It was a more consistent and controlled way to manage identity across a complex public sector environment.
How Much Identity Work Is Hiding Between Your Systems?
If onboarding, role changes and offboarding still depend on manual tasks and service desk tickets, we can help you identify where lifecycle automation could have the greatest impact.